Can your notes app read your notes?
Is Notion private? Can Google Keep, Apple Notes or Evernote read your notes? A fair, sourced comparison of who holds the key in 10 notes apps.
On this page
Can Notion read your notes? Technically, yes. Notion encrypts your data on the way to its servers and on its disks, but Notion holds the keys, so its systems can decrypt what you write. The same is true by default for Google Keep, Evernote, Microsoft OneNote and Apple Notes with standard iCloud settings. Apps that use end-to-end encryption by default, such as Standard Notes, Notesnook, Obsidian Sync and Cappa, can't read your notes, because only your devices hold the key.
"Is Notion private?" has a longer answer, and it is not a scandal. Holding the key is what lets these apps offer server search, easy sharing, AI features and a simple "forgot password" link. Below is a fair comparison of who holds the key in ten notes apps (ours included), checked against each vendor's own documentation as of September 2026, plus four questions you can ask about any app.
Who holds the key decides who can read
There are three layers of "encrypted," and the guide to end-to-end encrypted notes explains them in detail. In short:
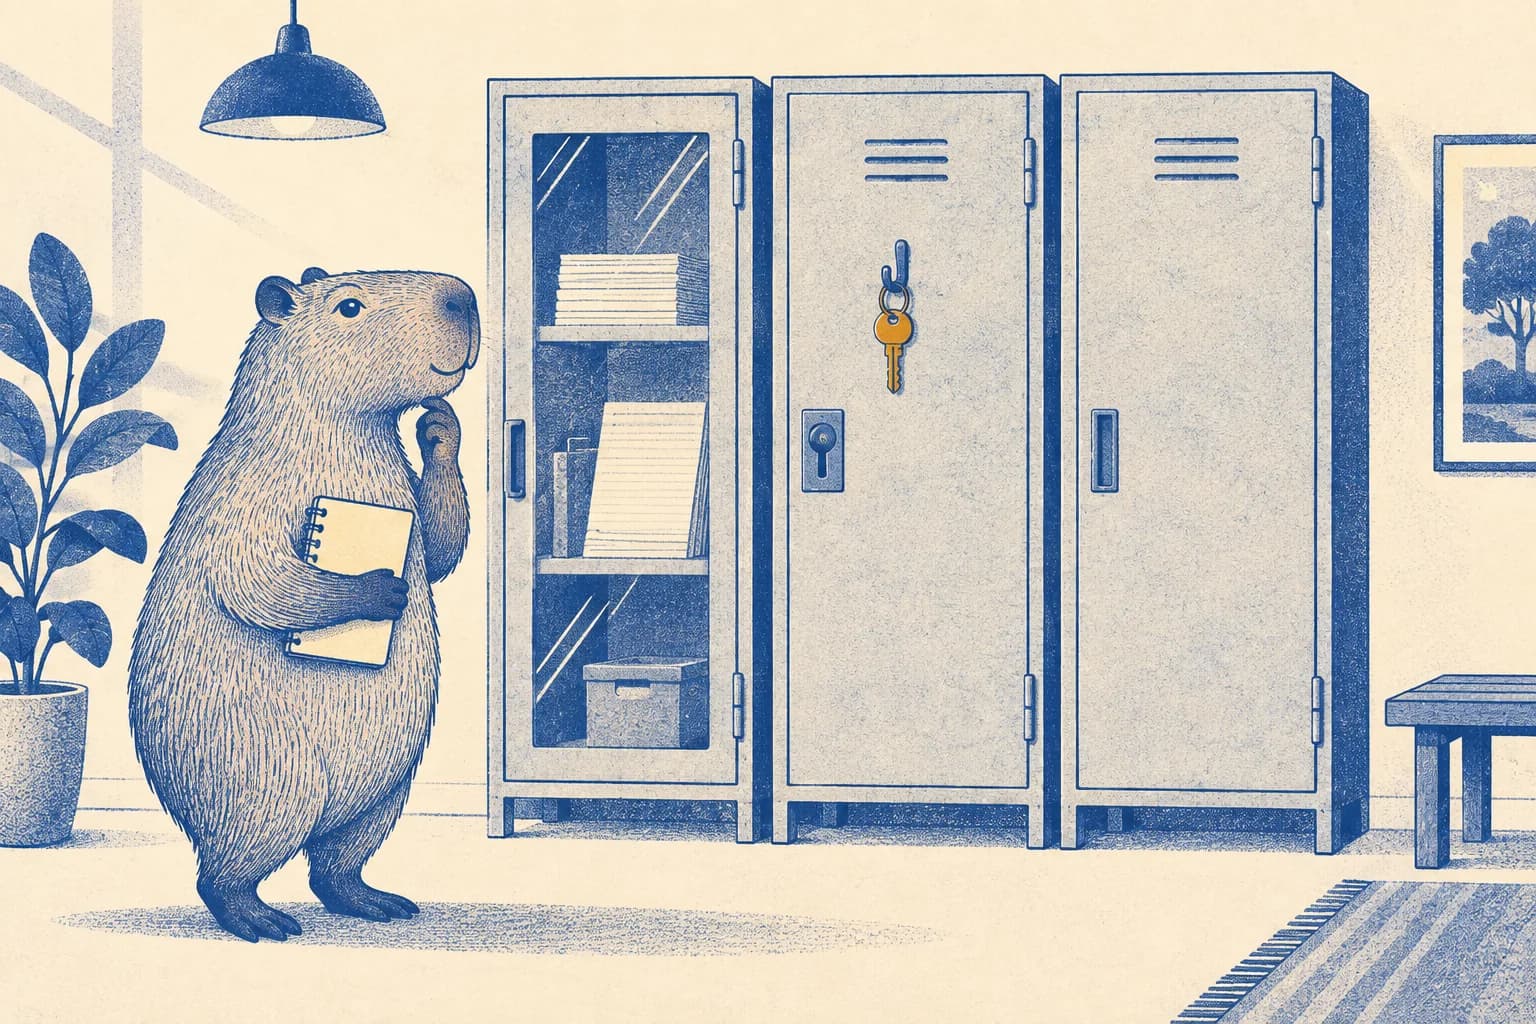
Glass door
Stored unencrypted. Anyone with access to the disk or files can read it.
Key on the hook
Encrypted in transit and at rest, but the company holds the key. It can decrypt when it needs to.
Sealed, key with you
End-to-end encrypted. The company stores ciphertext and has no key.
Almost every serious notes service today is at least the middle locker. That protects you well against a thief on public Wi-Fi or a stolen server disk. It does not stop the company itself, a legal demand served on the company, or someone who breaks into the company's systems deeply enough to use its keys.
Notes apps compared: who holds the key
This table summarizes each vendor's own documentation, as of September 2026. "Ciphertext only" means data is encrypted on your device before it leaves, so it stays encrypted in transit and at rest. Vendors change products, so follow the links to check the current wording.
| App | In transit | At rest | End-to-end | Who can decrypt by default |
|---|---|---|---|---|
| Notion | TLS 1.2 or newer | AES-256 | No | Notion |
| Google Keep | HTTPS and TLS | AES-256 (Google-wide statement) | No | |
| Apple Notes, standard iCloud | Yes | Yes | Locked notes only | Apple, except locked notes |
| Apple Notes with Advanced Data Protection | Yes | Yes | Yes, opt-in (some metadata excluded) | Only your devices |
| Evernote | TLS | AES-256, Google-managed keys | Only text you encrypt by hand on desktop | Evernote |
| Microsoft OneNote | TLS | AES-256 per file in OneDrive | Only password-protected sections | Microsoft |
| Obsidian, no sync | Not sent anywhere | Plain files on your device | Not applicable | Anyone who can open the folder |
| Obsidian Sync | Ciphertext only | Ciphertext only | Yes, by default (standard encryption is an option) | Only you, in the default mode |
| Standard Notes | Ciphertext only | Ciphertext only | Yes, by default | Only you |
| Notesnook | Ciphertext only | Ciphertext only | Yes, by default | Only you |
| Joplin | Depends on your sync service | Depends on your sync service | Opt-in | Your sync provider, until you turn it on |
| Cappa | Ciphertext only | Ciphertext only | Yes, always | Only you |
For Google Keep we could not find a Keep-specific security page. The at-rest statement ("All data that is stored by Google is encrypted at the storage layer using the Advanced Encryption Standard (AES) algorithm, AES-256") comes from Google Cloud documentation. Google's optional client-side encryption for business accounts lists Drive, Docs, Gmail, Calendar and Meet, and we found no mention of Keep.
Can Notion read my notes?
Notion's help center says data in transit is "encrypted using TLS 1.2 or greater" and customer data "is encrypted at rest using AES-256." Its security pages don't describe end-to-end encryption. Notion also says its employees "will only ever access your data for the purposes of troubleshooting problems or recovering content on your behalf" (Notion Help Center).
So is Notion private? From other people, yes, reasonably: your pages are encrypted on the network and on disk, and access is restricted. From Notion itself, no, not in the cryptographic sense. That is the design that lets Notion search your whole workspace on its servers, share pages with a link, let teammates edit at the same time and run Notion AI over your content. Notion states that by default neither it nor its AI subprocessors train models on customer data (Notion AI security practices). That is a policy promise, not a technical barrier, and it may be a perfectly acceptable one for work documents.
Are Apple Notes encrypted?
Yes, but how much depends on two settings.
- Standard iCloud data protection (the default). Apple lists Notes as encrypted "in transit & on server," with the keys stored by Apple. In Apple's words, the keys "are secured in Apple data centers, so Apple can decrypt your data on your behalf" (Apple Support).
- Locked notes. A note you lock with your device passcode or a separate notes password is end-to-end encrypted. Apple's Platform Security guide says the key is derived from your passphrase with PBKDF2 and the note is encrypted with AES-GCM. There are limits: you can't lock notes that you share or that contain tags, PDFs, audio or video, and if you forget a separate notes password, Apple can't help you get those notes back.
- Advanced Data Protection. This optional iCloud setting makes Notes end-to-end encrypted, with keys only on your trusted devices. You must set up a recovery contact or recovery key first. Some metadata stays under standard protection, including when a note was created, modified or last viewed, and whether it is pinned.
If you use Apple devices only and turn on Advanced Data Protection, Apple Notes is a strong private option with no extra app.
Is Google Keep encrypted?
Google Keep is encrypted in transit and at rest, like other Google services, and Google holds the keys. We could not find any end-to-end encryption option for Keep in Google's documentation, and Keep is not among the services covered by Google Workspace client-side encryption.
In practice, Keep is a quick, well-integrated notepad protected by your Google account's security. Treat anything in it as readable by Google's systems. Don't store passwords or recovery codes there.
Evernote and OneNote: a lock for part of a note
Both apps protect your notebooks the middle-locker way and add a small end-to-end lock you apply by hand.
- Evernote encrypts data at rest with AES-256 using "Google-managed encryption keys" and forces HTTPS for its services (Evernote Security). In its desktop apps you can select text and choose Encrypt text. Evernote says it uses AES with a 128-bit key derived from your passphrase with PBKDF2, and that it never receives the passphrase. Everything else in the note stays readable by Evernote.
- Microsoft OneNote notebooks usually live in OneDrive, where each file is encrypted at rest with its own AES-256 key, and those keys are protected by master keys in Azure Key Vault (Microsoft Support). You can password-protect a section, which uses 128-bit AES. If you forget that password, "not even Microsoft Technical Support" can unlock it, and protected sections are left out of notebook search until you unlock them.
These partial locks are useful for a few sensitive lines. They are easy to forget, though, and the rest of your notebook remains readable by the provider.
Obsidian, Standard Notes, Notesnook and Joplin
These four take different paths to the sealed locker.
- Obsidian stores notes "as Markdown-formatted plain text files" in a folder on your device (Obsidian Help). Without sync, nothing goes to Obsidian's servers, and protecting the folder is up to your device, such as full-disk encryption. With the paid Obsidian Sync, end-to-end encryption is the default, using AES-256 in GCM mode with a key derived by scrypt. You can instead choose "standard encryption," where Obsidian manages the key (Obsidian Sync security).
- Standard Notes encrypts all notes and tags end to end by default with XChaCha20-Poly1305, and turns your password into a key with Argon2 (Standard Notes Help).
- Notesnook encrypts everything on your device by default with XChaCha20-Poly1305 and derives the key with Argon2i; its help page says the server "stores ciphertext it cannot open" (Notesnook Help).
- Joplin syncs through a service you choose, such as Joplin Cloud, Dropbox, OneDrive, Nextcloud or WebDAV, and can encrypt notes end to end before they leave your device. Its documentation says end-to-end encryption "needs to be manually enabled on a single device first," and that the password "cannot be recovered" (Joplin E2EE).
All of these apps still show their servers some metadata, such as item identifiers and sizes. How much varies, and not every vendor documents it in detail.
Where Cappa fits, and what it gives up
Cappa, the encrypted notes app we build, is in the sealed-locker group. Every note, including its title, tags and attachments, is encrypted in your browser with AES-256-GCM before it syncs. The key is a random vault key that only your master password (stretched with Argon2id) or your recovery code can unlock. The server stores ciphertext and never receives your password, your recovery code or your vault key. (AES-256-GCM explained without math covers the cipher.)
It would be unfair to list only the upside. These are Cappa's trade-offs today:
- Invite-only. You can't register freely; an administrator sends an invitation. You can try the full editor in a demo that keeps everything in one browser tab.
- No password reset. If you lose both your master password and your recovery code, nobody can decrypt your notes. Using the recovery code also requires an administrator to open a 60-minute recovery window.
- Metadata is visible. The server sees your email, sessions with IP address and browser, devices, and each note's size and timestamps. The email provider that sends Cappa's security notices learns the kind and time of those events, such as a password change.
- No sharing or collaboration. Cappa is a notebook for one person.
- You trust the web app's code. Cappa runs in the browser, and the browser downloads the app from Cappa's server. A compromised server could send modified code that captures your password when you next unlock.
Four questions to ask any notes app
You don't need to read the source code to judge an app. Ask these:
- Who holds the key? Look for "encrypted on your device" or "we can't read your notes." "Encrypted in transit and at rest" alone means the company holds it.
- Is end-to-end encryption on by default, and does it cover everything? A locked note, a protected section or an opt-in setting protects only what you remember to lock. Check titles, tags and attachments too.
- What happens if I forget my password? If support can restore your notes by email, the company can decrypt them. If the answer is "use your recovery key or they are gone," that is a sign of end-to-end encryption.
- How would I leave? Encryption protects you from the company; export protects you from being stuck with it. Apps that store or export notes as plain Markdown files let you move to another app, or read your notes in any text editor, without a converter. Obsidian keeps Markdown files natively, and Cappa exports each note as a Markdown or text file.
A fifth, bonus question for the long term: does the app keep working when the company's servers don't? Local-first apps keep a full copy on your device, so an outage or a shutdown doesn't take your notes with it.
FAQ
Is Notion end-to-end encrypted?
No. Notion encrypts data in transit with TLS 1.2 or newer and at rest with AES-256, and it holds the keys. Its help center says employees access data only for troubleshooting or recovering content on your behalf. That is a policy safeguard, not end-to-end encryption.
Are Apple Notes end-to-end encrypted?
Locked notes are, whether you lock them with your device passcode or a separate password. All other notes are end-to-end encrypted only if you turn on Advanced Data Protection for iCloud. With standard protection, Apple holds the keys and can decrypt your notes.
Is Google Keep safe for sensitive notes?
Keep is protected by encryption in transit and at rest and by your Google account's security, which is solid against outsiders. It has no end-to-end encryption option that we could find, so Google's systems can read your notes. For passwords, recovery codes or anything highly sensitive, use a password manager or an end-to-end encrypted app.
What is the most private notes app?
There isn't one answer, because it depends on what you need. If you mainly want privacy from the provider, pick an app where end-to-end encryption is on by default and covers whole notes, such as Standard Notes, Notesnook, Obsidian with Sync, Apple Notes with Advanced Data Protection, or Cappa. Then check what metadata it keeps, how you would recover access and how easily you could export your notes.